
Master Your Attack Surface: Deterministic Breach Prevention meets Customizable Risk Intelligence
The modern Security Operations Center (SOC) is fighting an asymmetric war. Adversaries are bypassing Multi-Factor Authentication (MFA) with stolen session cookies, while legacy security scanners drown defenders in generic, uncontextualized alerts. The result is a "Contextual Certainty Deficit" that leaves organizations exposed and analysts burned out.
Today, ThreatNG is releasing a triad of major platform enhancements designed to break this cycle. We are putting organizations back in the driver's seat by giving them the tools to define their perimeter, uncover hidden identity threats, and score risk based on their unique business reality.
Here is what is new in the ThreatNG platform:
The Breach eXposure Module: Neutralizing MFA Bypass Attacks
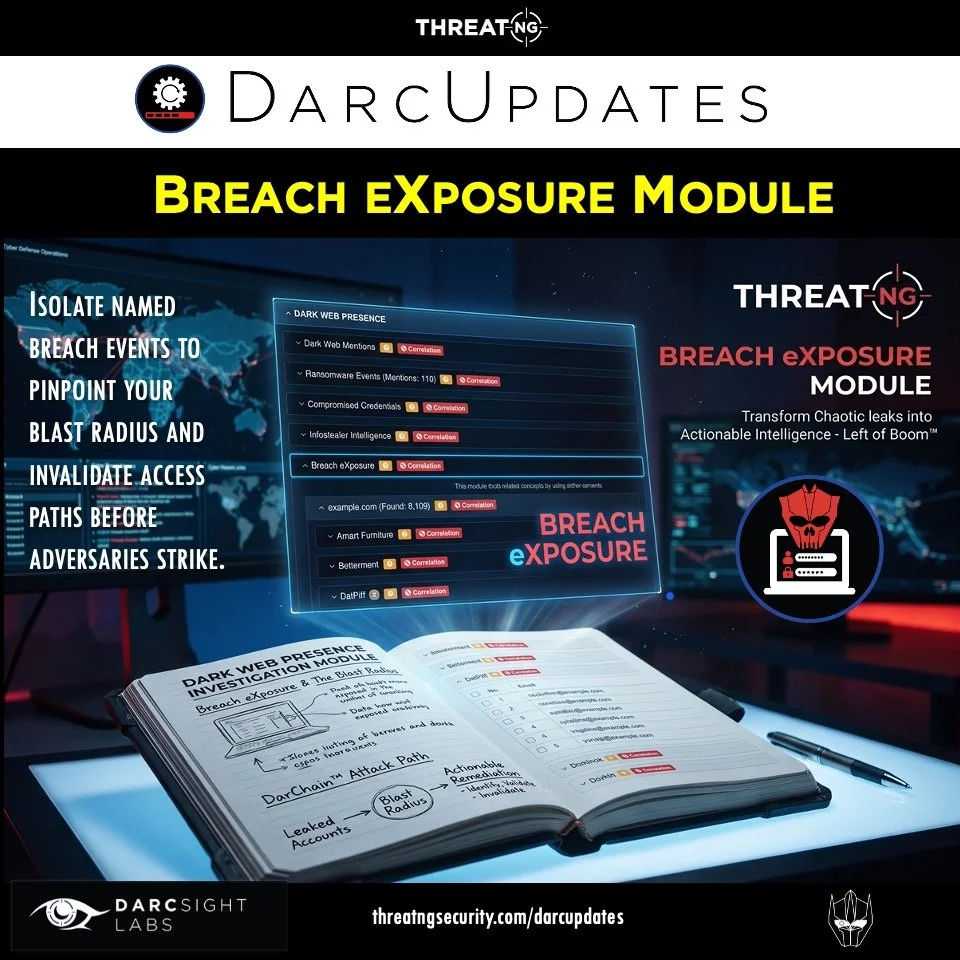
Legacy dark web monitoring gives you a "pile of bricks": massive, chaotic lists of historical data dumps. The new Breach eXposure Module (now natively integrated into our Dark Web Presence Investigation Module and powered by the DarCache Breach eXposure repository) delivers the blueprint.
Today, stolen passwords and live session cookies are the primary access vectors, appearing in 86% of corporate breaches and letting attackers bypass MFA entirely. The Breach eXposure module isolates specific, named breach events to identify exactly which of your organizational accounts are in the blast radius. This turns chaotic credential leaks into verified, actionable intelligence, giving your IAM teams the deterministic proof they need to invalidate access paths before adversaries can execute an exploit chain.
Risk Scoring and Configuration: Security on Your Terms
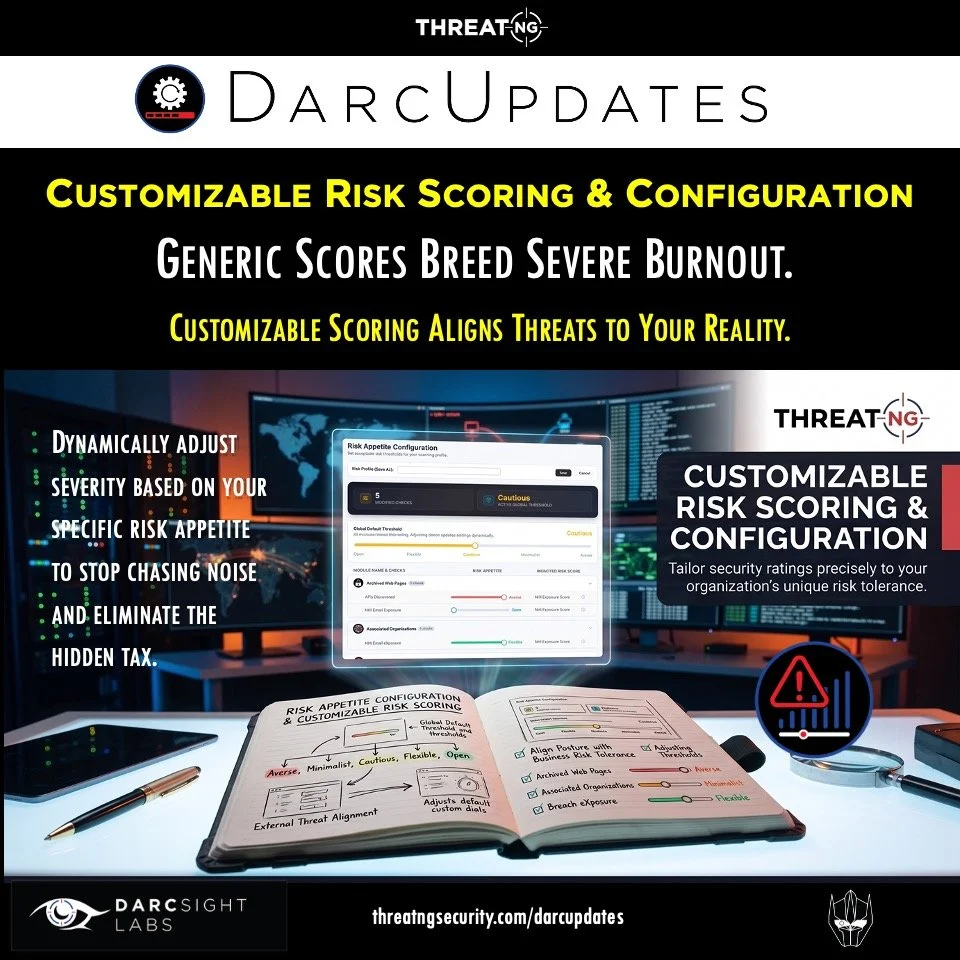
A CVSS 9.8 vulnerability on a forgotten sandbox server does not carry the same business risk as a 9.8 on your primary payment gateway. Yet, most rating platforms give you a generic, one-size-fits-all score.
With Customizable Risk Configuration and Scoring, ThreatNG introduces Contextual Risk Scoring. You can now align your security ratings precisely with your organization’s specific risk tolerance, whether Averse, Minimalist, Cautious, Flexible, or Open. By dynamically adjusting the weighting and severity of identified vulnerabilities based on your specific operational environment, you instantly eliminate the "Hidden Tax on the SOC". Your team stops chasing generic alerts and focuses strictly on the threats that violate your designated risk appetite.
Enhanced Dynamic Entity Management: Absolute Discovery Precision
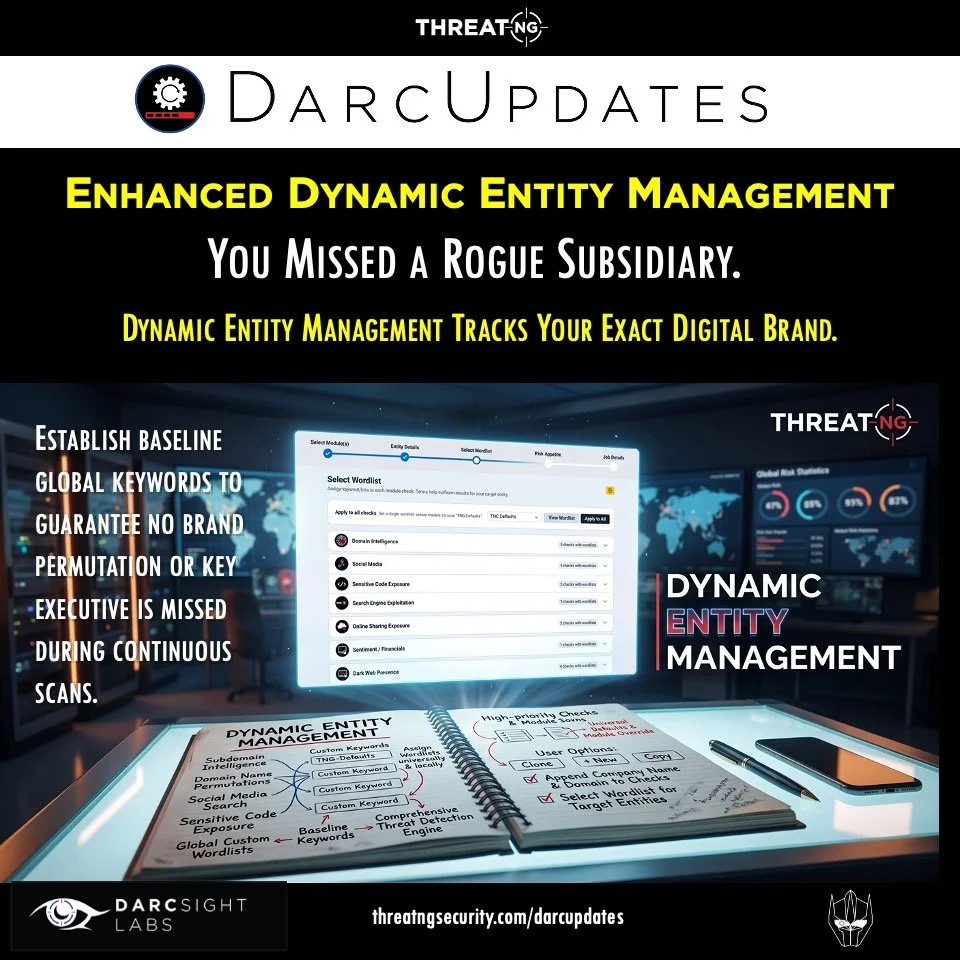
To protect your brand and find your exposures, your intelligence engine needs to know exactly what to look for. Our enhanced Dynamic Entity Management revolutionizes how you track your digital footprint.
With centralized global wordlist settings, users can now set baseline keywords across all investigation modules, including Sensitive Code Exposure, Dark Web Presence, and Social Media, while keeping granular, module-level overrides. Contextual terms, such as your company or domain name, are intelligently appended to checks by default, ensuring you don't miss any subsidiary, brand permutation, or key executive during continuous external investigations.
The ThreatNG Symphony: How It Works Together
These features aren't isolated updates; they form a cohesive defense mechanism.
It starts with Dynamic Entity Management, where you define your global footprint so ThreatNG knows exactly which assets, brands, and people to monitor. As ThreatNG scouts the perimeter, the Breach eXposure Module detects whether any of those entities have active session cookies or credentials circulating in a named breach event. Finally, Customizable Risk Scoring evaluates that exposure against your business context—instantly escalating a critical threat if you are "Risk Averse," or dynamically adjusting priority if it involves a "Flexible" development environment.
Stop settling for generic scores and reactive alerts. Experience Contextual Certainty with ThreatNG.